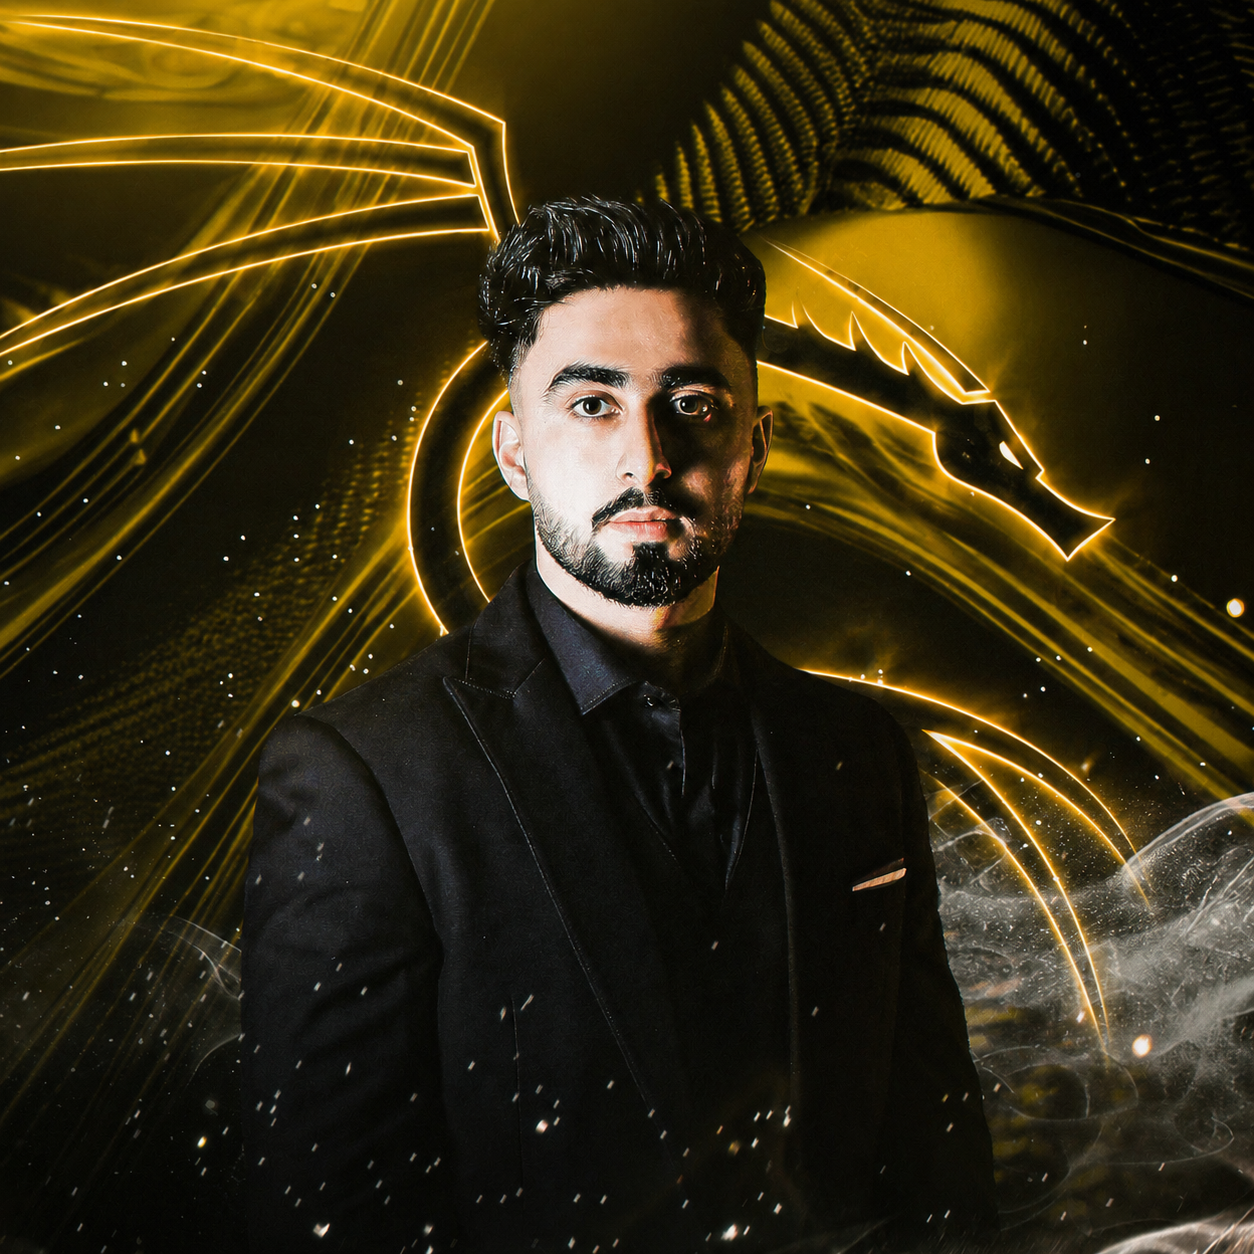
I am a cybersecurity practitioner focused on Penetration Testing and Cybersecurity, with hands-on experience across offensive security, vulnerability assessment, reconnaissance, and security reporting.
My penetration testing work includes network and web application testing, Active Directory security, Windows/Linux exploitation, privilege escalation, post-exploitation, vulnerability validation, and attack-path analysis. I have worked with tools and techniques including Nmap, Nessus, Burp Suite, Metasploit, Wireshark, BloodHound, Responder, mitm6, Mimikatz, Impacket, Kerberoasting, SMB relay, credential attacks, and related offensive security methodologies.
My OSINT experience includes open-source intelligence gathering, online research, source validation, digital footprint analysis, reconnaissance, information correlation, and structured intelligence reporting. I focus on identifying relevant information, validating sources, connecting technical findings, and presenting results clearly and professionally.
I hold the Practical Network Penetration Tester (PNPT), Practical OSINT Research Professional (PORP), Practical Junior Penetration Tester (PJPT), and CompTIA A+ certifications.
My approach to cybersecurity is based on understanding how attacks work, validating findings beyond automated tools, identifying root causes and attack paths, assessing security impact, and translating technical results into clear, actionable reports and remediation recommendations.
I continue to develop my expertise through hands-on labs, security research, practical certifications, technical projects, and real-world cybersecurity work, with a long-term focus on penetration testing, offensive security, OSINT, and threat intelligence.